Skip to content

Real end-to-end encryption.Nothing else compares.

Every file in DekkoCORE is encrypted on the device before it's uploaded. Only the people it's shared with can open it. Not even DekkoSecure can read it.

End-to-end encryptedNo keys to manageNo HSMs or BYOKZero-knowledgeAI-resistantSovereign AU · US · CAIRAP PROTECTEDITSG-33 aligned

Only the people you share withcan open your files.

Most secure file-sharing platforms keep keys where someone other than your users can reach them. DekkoCORE handles every key automatically and keeps them out of everyone else's reach.

What other platforms rely on

  • Hardware security modulesKeys sit in hardware you have to buy, rack and maintain. The platform still decrypts files on its servers to serve them.
  • Bring your own keyYou hold the master key. The service still uses it to decrypt your files whenever it needs to read them.
  • Private cloud and on-premisesDedicated infrastructure to deploy, patch and staff. Readable files sit on servers your team now has to defend.
  • “Private content networks”More infrastructure and key servers for your team to run. The trust and the responsibility land back with IT.

DekkoCORE

End-to-end encryption is built into the platform.

  • Files are encrypted on the sender's device and decrypted only on the recipient's
  • Keys are handled automatically in the background. People just sign in, upload and share
  • Servers, staff and cloud providers only ever handle ciphertext
  • No HSMs, key servers or key ceremonies to buy, deploy or run

The test

Can the provider, its cloud host or your own administrators read a file without a user's key?

With DekkoCORE, no one can.

AI changes attacks.It doesn't change the maths.

  1. Attacks now move in minutes

    AI agents can find and exploit software vulnerabilities almost instantly.

  2. Only ciphertext to work with

    DekkoCORE stores only encrypted data and never has the keys to open it.

  3. Brute force goes nowhere

    Guessing a key would take all the world's computing power an astronomical amount of time.

ai-agent vs end-to-end encryption
Simulated
  1. 00:00:01test start · ai agent given 1,284 encrypted files
  2. 00:00:04analysing file structure…
  3. 00:03:41searching for plaintext…
  4. 00:03:52searching for key material…
  5. 00:04:10sampling file contents…
  6. 00:04:11brief_to_counsel.pdf → U2FsdGVkX19vR3pLq8Hn2mZ0bE1x…
  7. 00:04:11evidence_0412.mp4 → 9fK2xQ7mLp0wE4rT8yU2iO6pA1sD…
  8. 00:04:12decryption keys found: 0
  9. 00:04:12fallback: brute-force decryption
  10. 00:04:13estimated time: longer than the age of the universe
  11. 00:04:13test complete · no readable data

The strongest security is the kind nobody has to think about.

  1. Receive an invite

    Someone shares a Hub or a file with you.

    Invitation

    Sally Smith invited you to Project Blue Book

    Accept invite
  2. Create an account

    Sign up with a passkey or TOTP MFA. Your keys are created in the background.

    Name
    Password
    Passkey Authenticator app (TOTP)
    Create account
  3. Collaborate

    Upload, edit and share as you normally would.

    brief_to_counsel.pdf
    access_review.docx
    SSMJOL

That's the whole user experience. Every file is end-to-end encrypted from the first click.

Handled automatically by the platform

  • Key generation
  • Public key infrastructure (PKI)
  • Key exchange between users
  • End-to-end encryption of every file and message

What nobody ever has to do

  • Generate, install or back up keys by hand
  • Manage certificates or key servers
  • Choose encryption settings
  • Remember extra security steps
  • Sit through security training

Four principles that apply to every file.

  1. Every channel encrypted

    Messages, eSignatures and video meetings are end-to-end encrypted the same way files are.

  2. Cryptographic separation

    Per-user and per-file cryptographic separation keeps every organisation's data isolated from every other's.

  3. Granular access control

    Seven permission levels, from listing only to full permissions, plus expiry dates and instant revocation.

  4. Nothing on your endpoints

    DekkoCORE runs in the browser, so there are no agents or plug-ins to deploy, patch or attack.
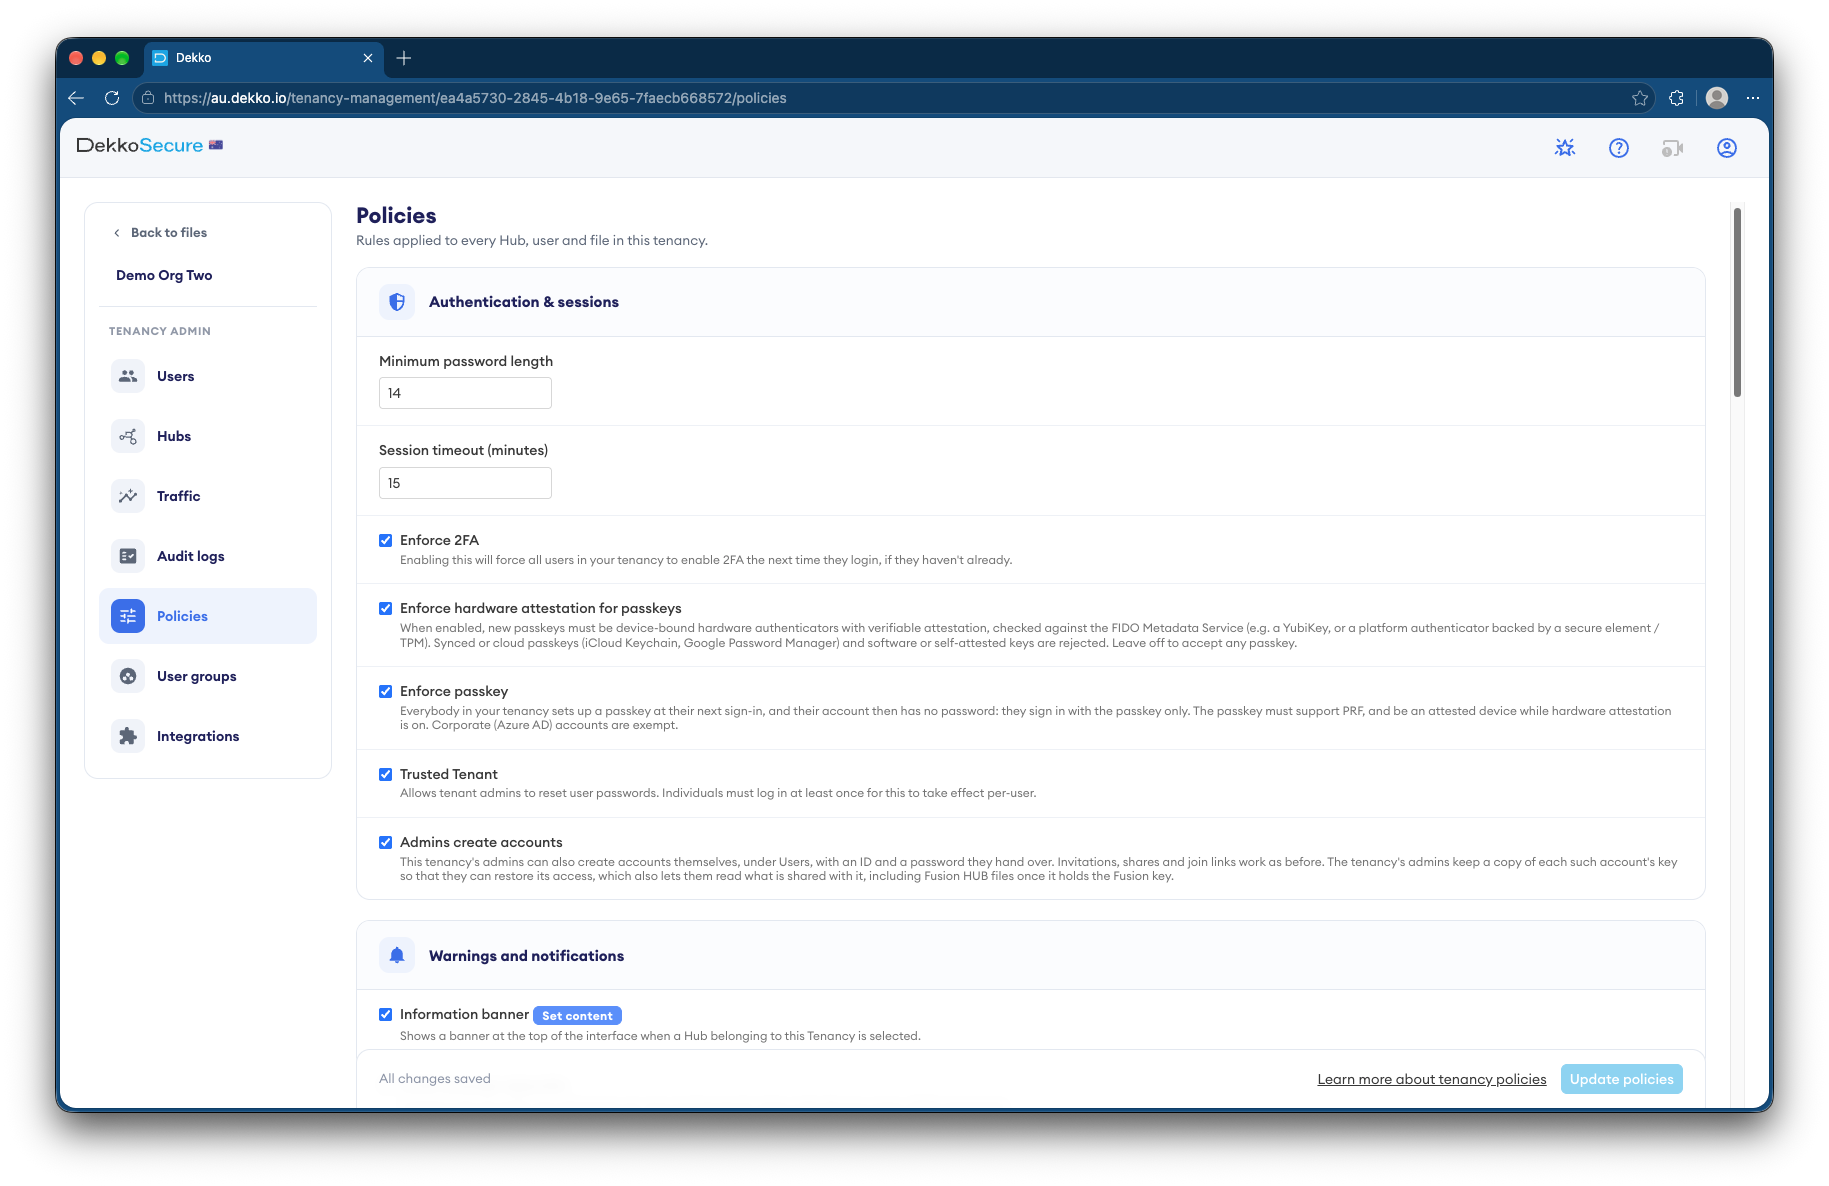
Enforce policy andprove compliance.

Tenancy policies

Tenancy policies

Enforce 2FA and passkeys with hardware attestation, and set password length and session timeouts.
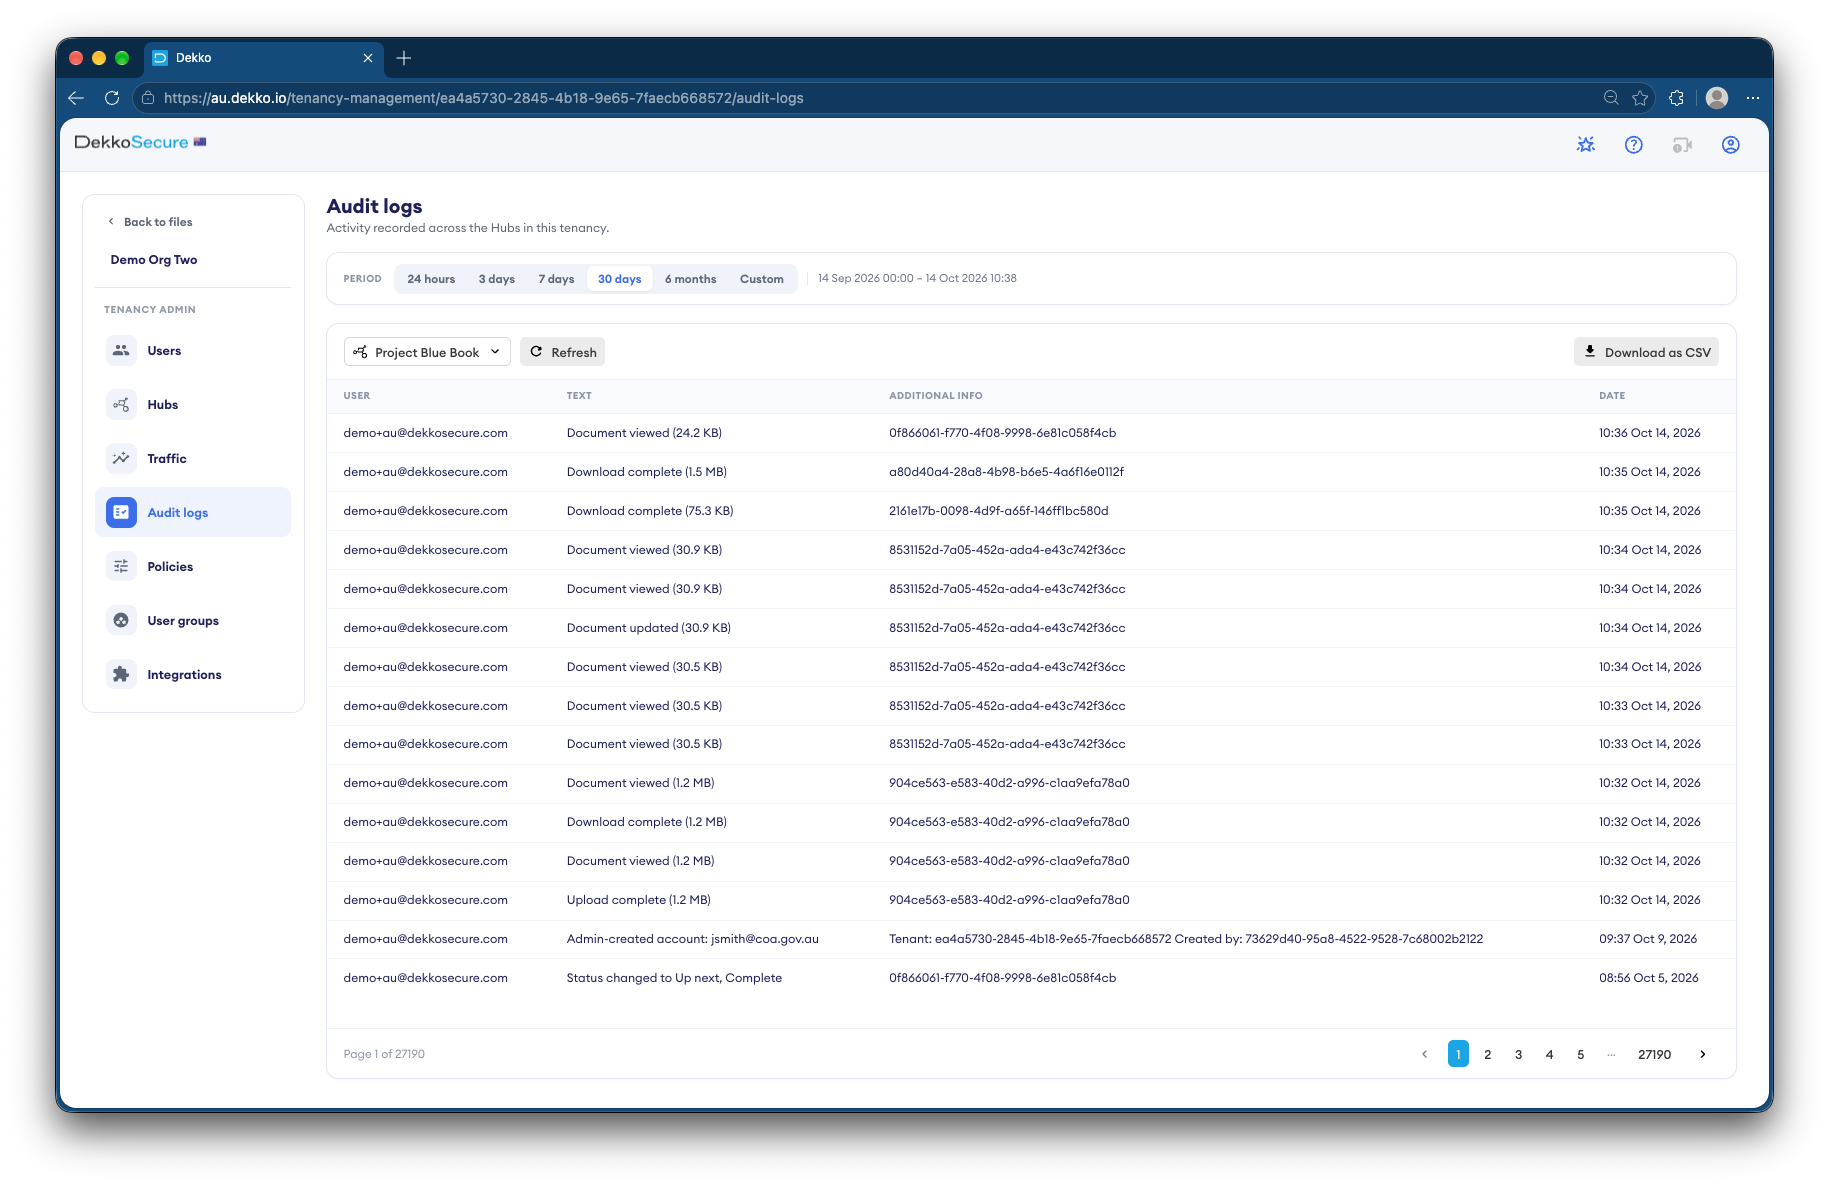
Audit logs

Audit logs

See activity across every Hub, filter it by Hub and period, and export it as CSV.

Audit integration

Plug into the tools your SOC already uses.

Azure Log Analytics

Stream audit events into your Log Analytics workspace.

Microsoft Entra ID

Tie audit activity to your Entra ID identities.

Malware scanning

Scan files with your cloud-based malware scanner over ICAP.

Your data stays in your country.

IRAP assessed to PROTECTED

Independently assessed under the Australian Government's Information Security Registered Assessors Program.

Australia

IRAP · PROTECTED

Canada

ITSG-33 aligned

United States

ITAR ready

Data centre compliance

  • ISO/IEC 27001
  • ISO/IEC 27017
  • ISO/IEC 27018
  • SOC 1
  • SOC 2 Type II
  • SOC 3
  • FedRAMP High
  • CSA STAR
  • PCI DSS

Independently verifiedand fully accountable.

  • Independently tested

    Independent third parties test our security claims.

  • Proven encryption standards

    We use established, publicly scrutinised cryptography, with no home-grown or proprietary algorithms.

Questions security teams ask us.

Is DekkoCORE an add-on for SharePoint, Dropbox or Google Drive?+

No. DekkoCORE is a standalone platform. Your files are stored, shared and worked on inside DekkoCORE, and the encryption is part of the platform itself rather than a layer over another service.

Can we see the IRAP assessment?+

Yes. Contact us and we'll share the assessment documentation with your security team.

Can DekkoSecure staff see our files?+

No. Files are end-to-end encrypted so only the people you share them with can open them. If you ever want help with a specific file, a user can choose to share it with our support team. That access covers only that content, is time-limited and is logged.

Where is our data stored, and can it leave the country?+

You choose Australia, the United States or Canada when your tenancy is set up. Your data is replicated within that country for resilience, and never moves to another region unless you authorise it or the law requires it.

How do users sign in, and can we enforce MFA?+

Your own users typically sign in with Microsoft Entra ID single sign-on. External users have their own DekkoSecure accounts, and you can require them to use TOTP two-factor authentication or passkeys, including hardware security keys.

Put us through your security review.

We welcome scrutiny. Book a session with our security team and ask for the architecture and assessment documentation.